
Kép
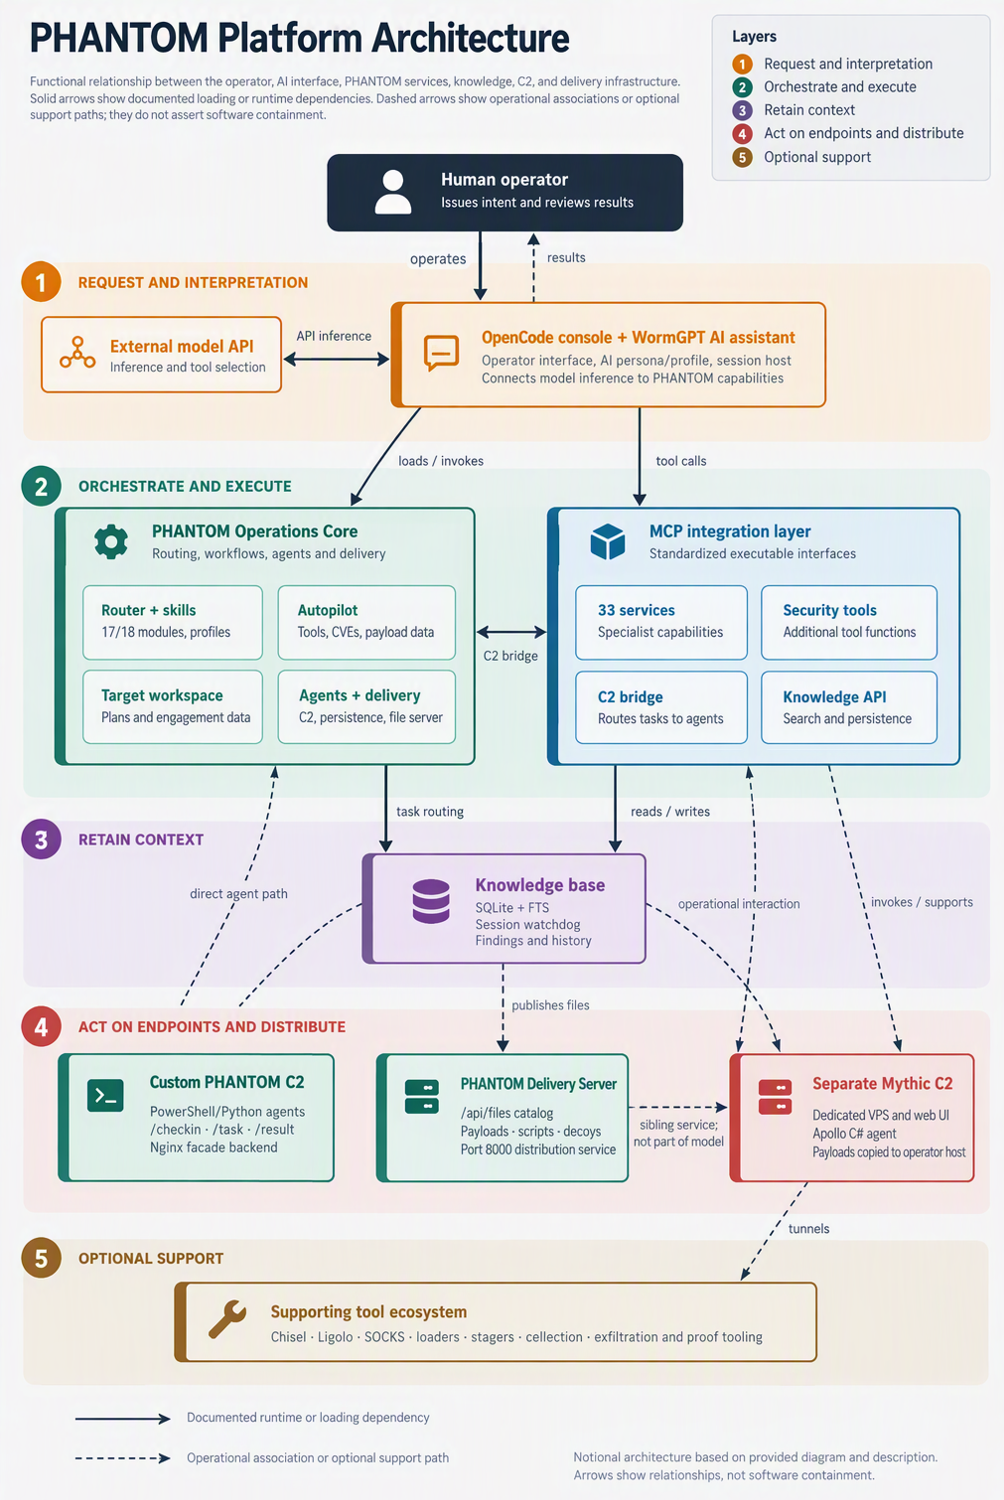

During adversary monitoring activities, the Atos Threat Research Center (TRC) identified an internet-accessible server linked to an operator associated with the INC ransomware ecosystem. A misconfigured HTTP service exposed a collection of command-and-control components, persistence and delivery scripts, tunneling utilities, data exfiltration tools, proof-of-compromise packages, victim management records, operational notes, and the Phantom AI-assisted offensive platform.
TRC collected evidence of active campaigns, operational logs, tooling, and details of the group’s techniques, tactics, and procedures. Within Phantom platform, OpenCode functioned as the operator interface, while WormGPT provided the AI assistant, persona, and operational guidance.
The exposed data provides insight into the operations behind a ransomware group, including reconnaissance, data theft, victim tracking, and ransom negotiations.
The environment also contained victim data from organizations across multiple sectors. This reflects a growing trend in ransomware operations, where threat actors focus on data exfiltration and extortion rather than file encryption.
Atos TRC contacted all victim organizations that could be reliably identified and independently confirmed from the recovered data. Notifications were provided to support incident response activities and to verify the accuracy of information contained within the exposed records.
The strongest evidence is not a single file. It is the convergence of three independent artifact classes:
TRC attributes this infrastructure to the INC ransomware operation with high confidence. Multiple victim organizations identified within the exposed data appeared on the INC Ransomware leak site in recent weeks, either as disclosed victims or as organizations listed for extortion. While the environment does not contain evidence linking every file or activity directly to the core INC team, the available evidence strongly indicates the server was operated by an INC-affiliated threat actor supporting INC ransomware operations.
The platform illustrates how AI is changing ransomware operations. The recovered evidence does not support the idea of autonomous AI conducting intrusions on its own. Instead, AI acted as a force multiplier for human operators. It reduced the effort required to research targets, develop scripts, analyze data, document findings, and coordinate activities across campaigns. By combining persistent knowledge, automation, and AI-assisted guidance, operators could work faster, maintain consistency, and reuse experience gained from previous intrusions.